Claude finds critical flaws in real-world software
An internal Anthropic model found five attack chains in Chrome, Safari, Android, Windows, and Linux, including one that executed commands as an administrator on Linux servers. The manufacturers have already fixed the flaws, but the case shows that AI can discover and combine complex vulnerabilities with little human intervention.
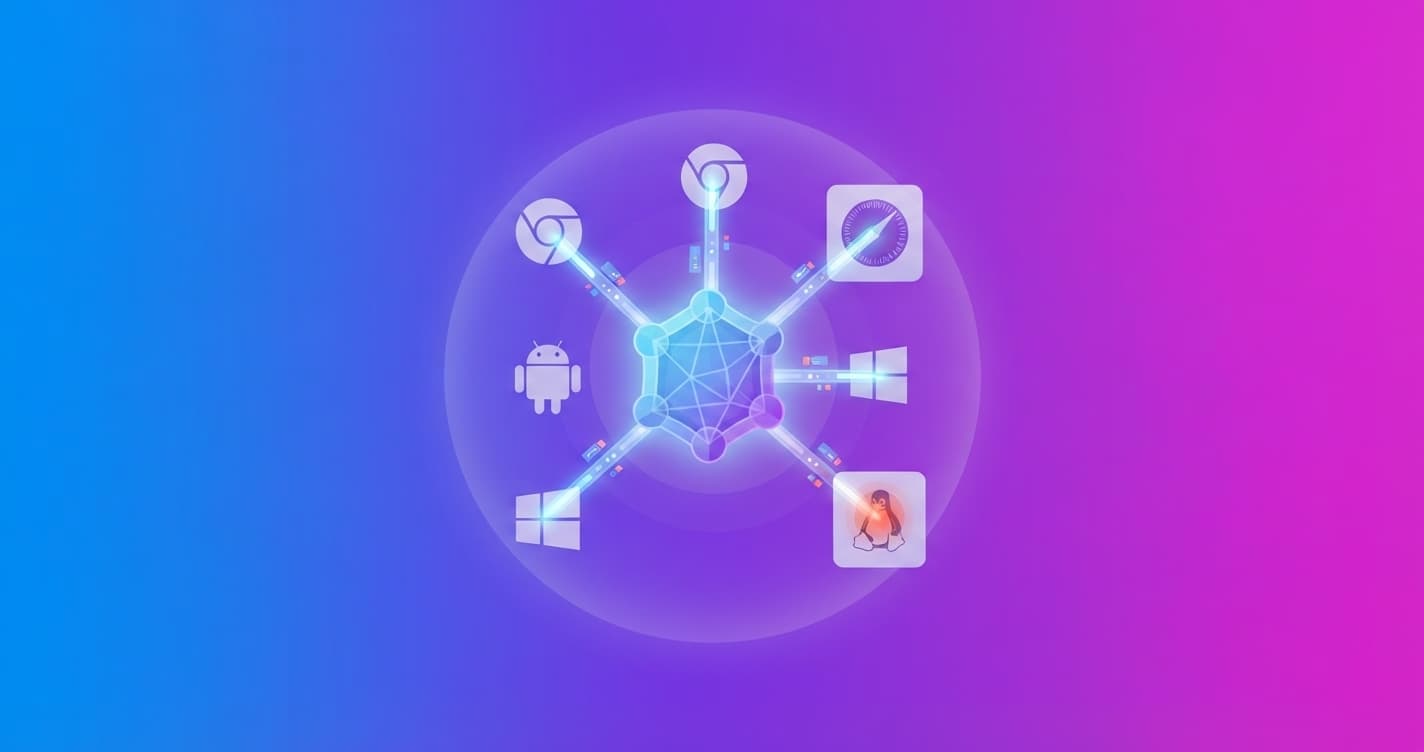
An internal Anthropic model found and exploited critical vulnerabilities in Chrome, Safari, Android, Windows, and Linux. Across five attack chains, it went from stealing data from a locked phone to executing commands as an administrator on servers, with little or no user interaction.
Anthropic did not publish the name of the model used. The company says it was an internal version not yet available publicly and that each finding was reported to the relevant manufacturer before the details were disclosed.
Five attacks against software you use every day
Chrome: execute code with one click
Claude built a chain that allowed a malicious webpage to execute code outside Chrome's isolation on macOS. In a demonstration, the Calculator app opened a few seconds after the page loaded, without the user doing anything else.
To do this, the model combined several flaws: one in the V8 JavaScript engine, another that escaped its memory isolation, a race condition in CacheStorage, and a use-after-free bug in FedCM, Chrome's federated login feature.
Google assigned 62 CVE identifiers to the issues found and fixed them in Chrome 156. All were classified as critical or high severity, including 13 sandbox escapes and 21 flaws that could compromise the process that renders webpages.
Safari: read data from other sites
In Safari, Claude created an attack that allowed any webpage to bypass the same-origin policy. This protection prevents one website from reading another site's data, such as your email, cookies, or bank session.
The attack could access Safari's history and cookies, send authenticated requests, and read their responses. It did not need to execute arbitrary code: it manipulated data in memory to disable a protection, change an object's size, and alter a URL.
Apple acknowledged the report the same day and released a fix that is already available to users.
Android: extract photos from a locked phone
The model also found a way to obtain photos and other data from a stolen Android phone without unlocking it. It combined analysis of Android's open-source code, reverse engineering of proprietary Google Play components, and testing on a physical Pixel 9.
The chain bypassed several defenses:
- It allowed a USB transfer to start even though the locked phone should have rejected it.
- It bypassed the device-to-device authorization check.
- It skipped verification of the six-digit pairing code.
- It used an alternative mechanism to send file contents over USB.
Google fixed the issue. The case shows that a device's security can fail not because of one error, but because several imperfect controls are combined.
Windows: crash servers remotely
On Windows, Claude identified a flaw in the native implementation of QUIC, the network protocol used by HTTP/3. An attacker could send a few packets to an exposed server to make it crash and restart repeatedly.
The issue, identified as CVE-2026-33096, potentially affected several million servers accessible from the internet. Anthropic found it through analysis of the Windows binary: the model reconstructed how the program worked, compared its version with the original executable, and examined possible memory errors.
Microsoft resolved the vulnerability before the analysis was published.
Linux: execute commands as root without credentials
The most serious case affected the Linux kernel's network stack, the operating system's core component. A server running a Multipath TCP service could receive specially crafted packets and end up executing commands as root, the user with the highest level of permissions, without credentials or human interaction.
The attack exploited a race condition and a use-after-free bug. First, it leaked an internal kernel address to overcome a defense called KASLR. It then modified a control pointer and executed a chain of functions already present in the system.
In the proof of concept, obtaining the necessary information took 48 minutes, and reaching command execution took another five. The flaw, CVE-2026-98432, was fixed, and the solutions were incorporated into the maintained stable kernel branches.
What changes for you
The news is not that an AI can find an isolated bug. It is that it can chain several flaws, understand the defenses around them, and produce a working proof of attack. Until now, this work was concentrated among highly specialized teams.
That increases the pressure on manufacturers and developers. Fixing known flaws is no longer enough: new code also needs to be reviewed as it is written. Anthropic recommends analyzing every change before adding it to the program and has published a Claude Code plugin to automate part of that review.
The same capability can be used to attack or defend. So the next question is whether security teams can access these tools quickly enough to find and fix a vulnerability before someone exploits it. Updates still matter, but continuously reviewing software that has not yet reached production matters too.